Svenska Dokumentmallar
GDPR Personal Data Breach Template Package 2026 – Word/PDF/Excel
GDPR Personal Data Breach Template Package 2026 – Word/PDF/Excel
 Downloading the template is available immediately after purchase. Our document templates are always delivered in customizable formats.
 If you are unsure which template is appropriate or how you should complete it, please see the relevant information under the 'Legal Information' tab in our main menu.
 Our templates are designed in accordance with current legislation and practice in each area to ensure that the documents you create are legally correct.


Couldn't load pickup availability
Personal Data Breach GDPR Template Package 2026 – incident report, IMY notification & 72-hour tool
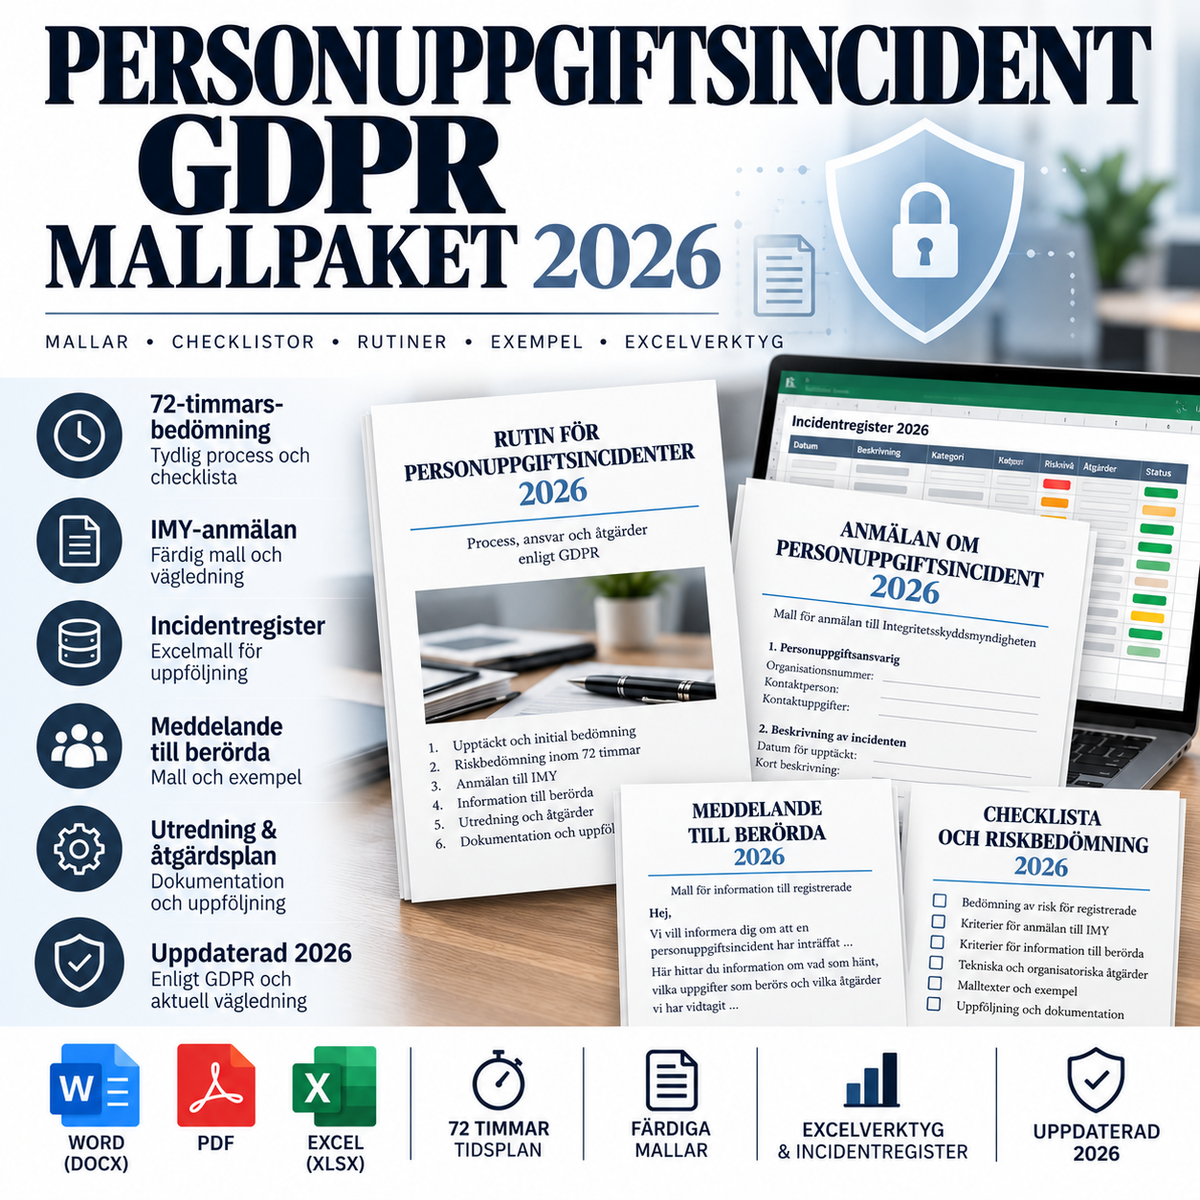
A complete template package for companies and organizations that need to detect, assess, document, and manage personal data breaches according to the GDPR. The package contains professional Word/PDF templates as well as an Excel tool for incident registers, 72-hour deadlines, risk assessments, IMY (Swedish Authority for Privacy Protection) notifications, information to data subjects, processor reporting, and post-incident analysis.
The GDPR requires that all personal data breaches be documented. A breach must be reported to the supervisory authority unless it is unlikely that it will result in a risk to the rights and freedoms of natural persons. If a notification is required, it must be made without undue delay and, where feasible, within 72 hours of the controller becoming aware of the breach.
Included – 9 files
- Personal Data Breach – Incident Report & 72-hour assessment, Word + PDF
- Notification to IMY – preparation documentation, Word + PDF
- Information to data subjects according to Article 34 GDPR, Word + PDF
- Procedure for personal data breaches / Incident Response Playbook, Word + PDF
- Excel tool with incident register, 72h status, risk classification, IMY log, data subjects, processor notices, measures, and post-incident analysis
Incident report with complete decision-making process
The main template helps the organization document the entire incident from initial detection to closure:
- time of incident, detection, and organization awareness
- automatic/clear 72-hour deadline
- classification as a confidentiality, integrity, or availability breach
- affected data subjects and personal data
- sensitive data, Article 10 data, protected personal data, and children/vulnerable individuals
- immediate containment and recovery measures
- risk assessment for the rights and freedoms of data subjects
- decision regarding IMY notification
- decision regarding information to data subjects
- root cause, corrective measures, and lessons learned
When should the breach be reported?
As a data controller, you must report the breach if it is not unlikely that it will result in a risk to the rights and freedoms of natural persons. If all information is not available within 72 hours, the information may be provided in phases without undue further delay. In the event of a late notification, the reasons for the delay must be documented.
The package therefore contains a separate IMY preparation template with the central information that needs to be collected before or during the reporting. The actual notification is made via IMY's current e-service or other channel designated by the authority.
High risk – information to data subjects
If the personal data breach is likely to result in a high risk, the data subjects must, as a general rule, be informed without undue delay. The package contains a ready-to-use and editable communication template with:
- clear description of what has happened
- what personal data is affected
- likely consequences
- implemented and planned measures
- practical advice to the data subjects
- contact details for the Data Protection Officer or other point of contact
The template also includes a check against Article 34 exceptions, for example, if the data was effectively encrypted, if subsequent measures eliminated the high risk, or if individual notification involves disproportionate effort.
Obligations of the processor
A processor must report a personal data breach to the controller without undue delay. The processor does not need to determine whether the incident entails such a risk that it must be reported to IMY – the primary responsibility for the risk and notification assessment lies with the controller.
The Excel tool therefore contains a separate register for processor notices with awareness time, initial report, time difference, missing information, and next update.
Excel – incident register with 72-hour check
The Excel file serves as a practical incident management tool and contains:
- dashboard with key performance indicators
- incident register
- 72-hour deadline and status On time / Urgent / Overdue
- risk classification based on probability and impact
- IMY notification register
- communication to data subjects
- processor reporting
- measures register
- Post-Incident Review / root cause analysis
- sources and legal references
All breaches must be documented
Even breaches that do not need to be reported to IMY must be documented. The documentation should, among other things, make it possible to verify that the organization has followed the GDPR and should also include the reasons for the decision not to notify or not to inform data subjects.
Common incidents for which the package can be used
- misdirected emails or documents
- phishing and compromised accounts
- ransomware and data breaches
- incorrect access rights
- lost computer, phone, or storage media
- accidental publication
- incorrect sharing via cloud service or link
- deletion or loss of personal data
- incident at a processor or subcontractor
Legal basis
The template package has been legally reviewed as of October 3, 2026, based on:
- GDPR Article 4(12)
- GDPR Article 33 – notification to the supervisory authority and documentation
- GDPR Article 34 – information to data subjects
- IMY's current guidance on personal data breaches and e-service
- EDPB Guidelines 01/2021 on Examples regarding Personal Data Breach Notification
During 2026, the EDPB also published a proposal for a common European breach-notification-template for public consultation. The legal accuracy of this package is not based on a consultation document that has not yet been fully implemented, but on current GDPR, IMY's current guidance, and adopted EDPB guidelines.
Please note
The package is a general compliance and documentation framework. An actual incident may simultaneously be covered by other reporting regulations, such as sector-specific requirements in finance, cybersecurity, healthcare, or public operations. Therefore, always check whether additional authorities, contracting parties, insurers, or other actors need to be informed.
Format: Word (DOCX) + PDF + Excel (XLSX)
Language: Swedish
Jurisdiction: Sweden / EU
Number of files: 9
Version: 1.0 – 2026-10-03