Svenska Dokumentmallar
CRA support period 2027 – security updates, customer information and lifecycle register | Word/PDF/Excel
CRA support period 2027 – security updates, customer information and lifecycle register | Word/PDF/Excel
- File format
- DOCX, PDF, XLSX
- Document language
- Five Swedish work templates + Swedish user guide + English User Guide for Swedish templates; Excel in Swedish
- Number of files
- 7
Digital download. No physical product is shipped.
Couldn't load pickup availability
About this template
How long must a manufacturer keep its digital product secure, and how is the end of support clearly communicated to the customer? With this specialist package, you document the expected period of use, support period, vulnerability management, security updates, customer information, and continued access to patches already released. Designed for Swedish manufacturers, product owners, development managers, PSIRT, and companies selling software or connected hardware in the EU.
Quick facts: 15 customer files: seven editable Word documents (DOCX), seven corresponding searchable and printable PDF files, and an Excel register (XLSX) with nine tabs. Five Swedish working templates, a Swedish user guide, and a separate English user guide for the Swedish templates. The PDF files are not interactive fillable forms.
Package contents
01 Support Period Assessment; 02 Security Update Procedure; 03 Customer Information and End of Support; 04 Component Dependencies and Version Tracking; 05 Support Termination and Archiving; 06 Swedish User Guide; 07 English User Guide – all seven in Word and PDF. In addition, 08 Excel – Support Period and Lifecycle Register. Total 7 DOCX + 7 PDF + 1 XLSX = 15 files.
What the files contain
Decisions and reasons for the expected product lifespan, upstream component support, applicability assessment, release/test evidence, patch archive, customer texts stating the end of support at least by month/year, continued access to older security updates, verification checklists, supporting references, and a consolidated Excel overview. Sources and clear legal limitations are included.
Who is the package suitable for?
For example, a Swedish supplier of connected sensors, a software company, a manufacturer with embedded third-party components, or a product team that must document its support policy ahead of the CRA's main application in December 2027.
Not suitable on its own if you need an actual SBOM generator, code analysis, security certification, penetration test, CE declaration, or formal mandatory reporting to a regulatory authority. The template cannot automatically determine the product's applicability or guarantee legal compliance.
File overview – what does the customer receive?
| File | Purpose | Format / language |
|---|---|---|
| 01 Support Period Assessment | Weigh actual expected use, user expectations, component support, and reasons for the chosen period. | Swedish · editable DOCX + searchable PDF |
| 02 Security Update Procedure | Record vulnerability case, test, release, secure distribution, customer advice, and patch access period. | Swedish · DOCX + PDF |
| 03 Customer Information and End of Support | Text fields for end of support, update paths, secure use, and pre-termination notice. | Swedish · DOCX + PDF |
| 04 Component Dependencies and Version Tracking | Assess components, third-party support, version risk, SBOM references, and actions. | Swedish · DOCX + PDF |
| 05 Support Termination and Archiving | Keep terminated active support, historical security updates, and technical documentation periods separate. | Swedish · DOCX + PDF |
| 06 Swedish User Guide | Workflow, source matrix, six realistic scenarios, and control questions. | Swedish · DOCX + PDF |
| 07 English User Guide | Explanation of the five Swedish working templates and their limitations. | English · DOCX + PDF; not English legal templates |
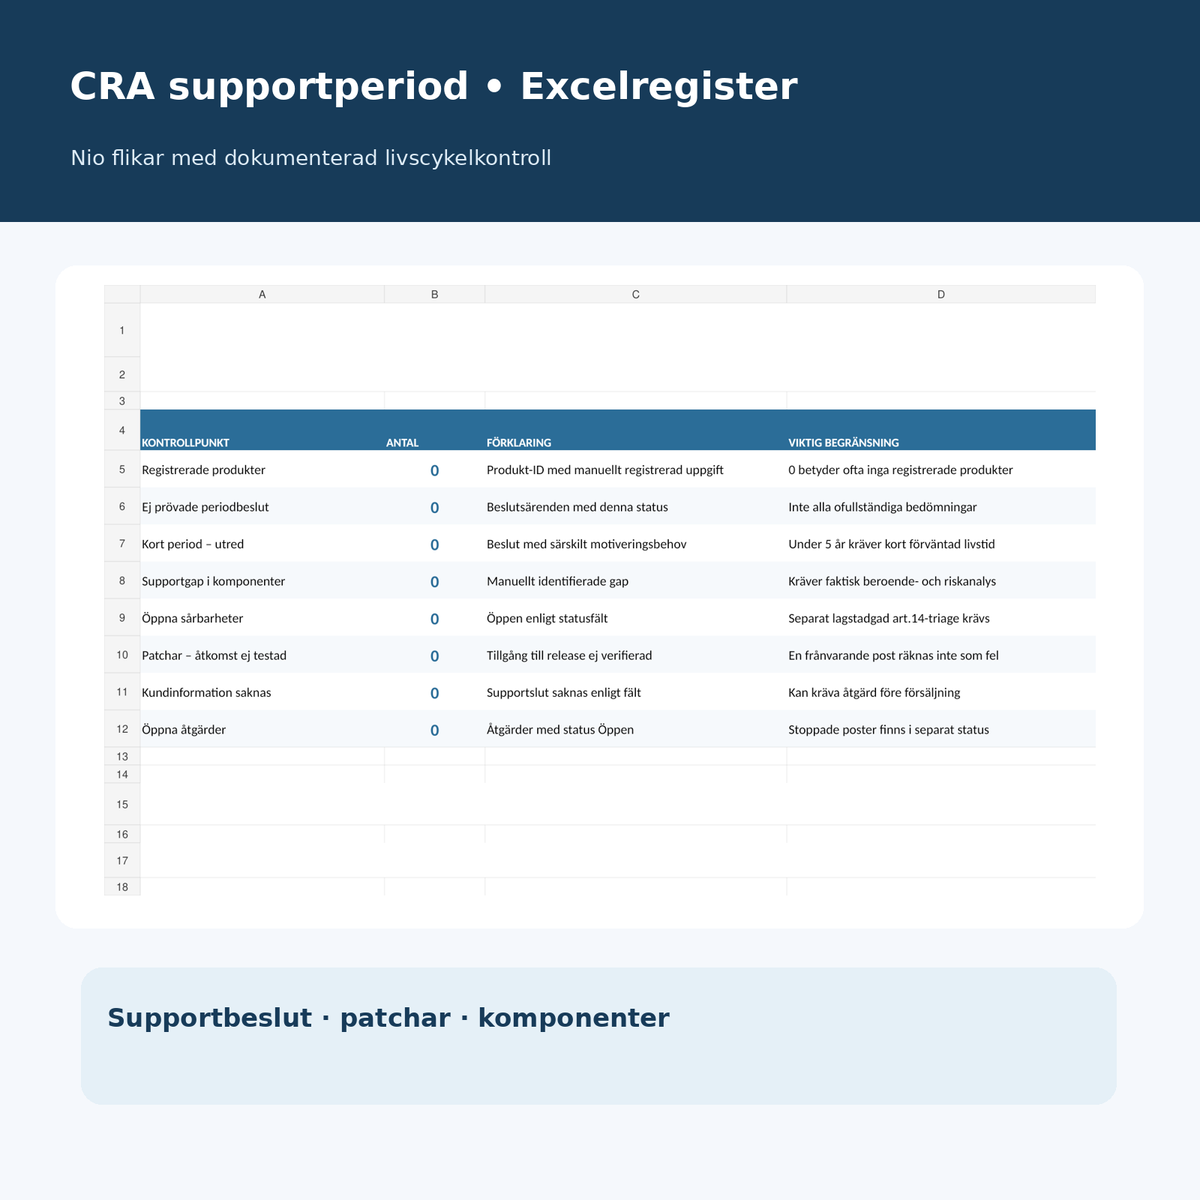
| 08 Excel Register | Administrative tracking of decisions, patches, components, vulnerabilities, customer information, and actions. | Swedish · editable XLSX |
Excel with nine tabs
Overview, Products, Period Decisions, Components, Vulnerabilities, Updates, Customer Information, Actions, and Read Me. Record, for example, which products lack a final support decision, short support periods that need to be tested, component gaps, open vulnerabilities, patches with unverified access, and missing customer information. The overview uses tested status formulas and contains no fictional test data.
Warning: Zero open cases may be due to no cases being registered. Excel is not a legal assessment engine, not a vulnerability scanner, and not an automatic approval.
How to use the documents
- Determine whether the manufacturer and product are covered by the CRA and whether other sector regulations are relevant.
- Document the product's expected period of use, customer expectations, and dependency components.
- Justify the support period – normally at least five years, but longer where the product's expected use requires it; shorter requires a justified shorter period of use.
- Approve responsibility, resources, vulnerability reception, patching, testing, and secure distribution.
- Clearly state the product's end of support at the time of purchase, at least with month and year, and provide relevant security information.
- Record the release date of each update and check continued access during the correct period.
- Document technical supporting evidence, evidence of information provision, and re-assessment under changed circumstances.
Legal basis and important dates
Regulation (EU) 2024/2847 – Cyber Resilience Act is the main source. According to Article 13.8, the manufacturer shall choose a support period corresponding to the product's expected period of use. As a general rule, this is at least five years, but a shorter period is possible if the product's expected use actually falls below five years. If the period of use is longer, five years may be too short. The basis for the assessment shall be included in the technical documentation.
Article 13.9: A security update made available during the support period shall be available for at least ten years after it is released, or longer if the remainder of the support period is longer. This is a rule regarding availability of the update itself – not a general requirement for ten years of active support.
Article 13.19 requires that the end date of the support period, at least month and year, be clearly stated at the time of purchase. Annex II points 7 and 8 cover, among other things, the type of support, update instructions, secure installation, and secure decommissioning. Annex I Part II covers vulnerability management and updates, including secure distribution and user information.
Dates: The main CRA product requirements begin to apply on 11 December 2027. Reporting obligations under Article 14 for certain actively exploited vulnerabilities and serious security incidents have already applied since 11 September 2026. Products, roles, transitional rules, applicability, and complementary guidance should be assessed for the relevant manufacturer. The EU Commission's CRA overview and guidance from 27 July 2026 provide additional support.
Difference from Mallbutiken's other CRA products
The existing CRA Compliance Package has a broad focus on risk assessment, SBOM, and incident requirements. This specialist product focuses on the legal and technical justification of the support period decision, customer information, and continued patch access. PSIRT incident reporting is handled separately. For general operational updates and change planning, the affected organization's own technical processes are also required.
Frequently asked questions
Must all products be supported for exactly five years?
No. The support period shall follow the expected period of use and is often longer than five years. A shorter period requires concrete evidence that the product is actually expected to be used for a shorter period.
Does the ten-year requirement mean we must release new patches for ten years?
No. Article 13.9 refers to continued access to patches that have actually been released during the support period. This is a separate issue from the length of the active support period.
What does the customer need to see at the time of purchase?
Among other things, the type of technical security support and end of support, clearly and understandably stated with at least month and year.
Can Excel determine if a patch meets the CRA?
No. Excel summarizes the manual fields that the organization fills in itself and contains no technical scanner or regulatory certification.
Are actual security updates or a machine-readable SBOM included?
No. Working templates for documentation and secure references are included. Actual development work, testing, and SBOM generation must be done separately.
Can the PDFs be filled in digitally?
They are searchable and printable but are not interactive PDF forms. Edit the documents in Word and Excel.
Are all documents translated into English?
No. Five Swedish working templates and Excel are in Swedish; one English user guide is included to explain the workflow.
Sources, review level, and version
Official sources: EU 2024/2847, EU Commission summary, implementation timeline, and 2026 guidance.
Product version: 1.0, 12 November 2026. Legal source control: AI-assisted with support from official sources. No independent external legal review, actual product security testing, regulatory review, or CE certification. The files are an adaptable work product and must not be marketed as verified compliance. Delivery via digital ZIP requires separate activation of the store's download function before publication.