Svenska Dokumentmallar
NIS2 Management Decision 2026 – Approval, Risk Acceptance and Annual Review | Word/PDF/Excel
NIS2 Management Decision 2026 – Approval, Risk Acceptance and Annual Review | Word/PDF/Excel
- File format
- DOCX, PDF, XLSX
- Document language
- Five Swedish workbooks Swedish user guide and English User Guide to Swedish workbooks; Excel in Swedish
- Number of files
- 7
Digital download. No physical product is shipped.
Couldn't load pickup availability
About this template
Does the board, CEO, or other competent management need to make and document actual decisions about the organization's cybersecurity? This niche Word/PDF/Excel package helps Swedish businesses move from risk reporting and proposed measures to traceable management decisions, resource allocation, conditional risk assessment, and follow-up in accordance with current law. It is not a new general information security policy.
Quick facts: 15 downloadable customer files: seven editable DOCX files, seven corresponding searchable but non-interactively fillable PDFs, and one XLSX workbook with nine tabs. Five Swedish work templates, one Swedish guide, and a separate English User Guide for the Swedish work documents. Version 1.0, November 12, 2026.
Package contents
01 Decision-making basis for management; 02 Management minutes and decisions; 03 Risk acceptance and deviation; 04 Security measure plan and budget; 05 Management follow-up and annual cycle; 06 Swedish user guide; 07 English User Guide. These seven documents are delivered in both Word and PDF formats. In addition, 08 Excel register for decisions, risks, measures, resources, and follow-up is included. Total 7 + 7 + 1 = 15 files.
What the files contain
Assessment of the operator's basis of applicability and regulatory scope, concrete decision wording for competent management, control of legally mandatory measures, documentation of residual risk without unauthorized waivers, responsibility and funding, evidence references, information needs, and follow-up.
For whom and in what situation?
Suitable for: a Swedish limited company, an economic association, a municipality/region, an authority, or another organization that has determined that it is affected by the Cybersecurity Act and needs to show how competent management makes and follows up cybersecurity decisions. The materials can be adapted to the organization's own decision-making structure.
Not suitable on its own: as legal evidence that the business is covered by NIS2, a complete risk analysis, an actually conducted security audit, a formal authority certificate, or a guarantee of legal compliance. An internal risk acceptance cannot replace binding security measures.
File by file
| Document | Practical task | Format and language |
|---|---|---|
| 01 NIS2 decision-making basis | Determine which operator, sector, and regulatory scope are intended; compile risks and proposed decisions. | Swedish – editable DOCX + searchable PDF |
| 02 NIS2 management minutes | Note the competent body, mandate, actual decisions on goals, measures, responsibilities, and resources, and adjust according to the organizational form. | Swedish – DOCX + PDF |
| 03 Risk acceptance and deviation | Distinguish an internally accepted residual risk from a legally binding measure; document escalation, conditions, and review. | Swedish – DOCX + PDF |
| 04 Security measure plan and budget | Link measures to the law's measure categories, system owners, schedules, and resources. | Swedish – DOCX + PDF |
| 05 Annual follow-up and management report | Evaluate effectiveness, risk changes, incidents, priorities, and new decisions. | Swedish – DOCX + PDF |
| 06 Swedish user guide | Step-by-step workflow and source matrix for the difference between legal requirements, regulations, and general advice. | Swedish – DOCX + PDF |
| 07 English User Guide | Explains the workflow and Swedish terms in English; does not translate the five Swedish work templates. | English – DOCX + PDF |
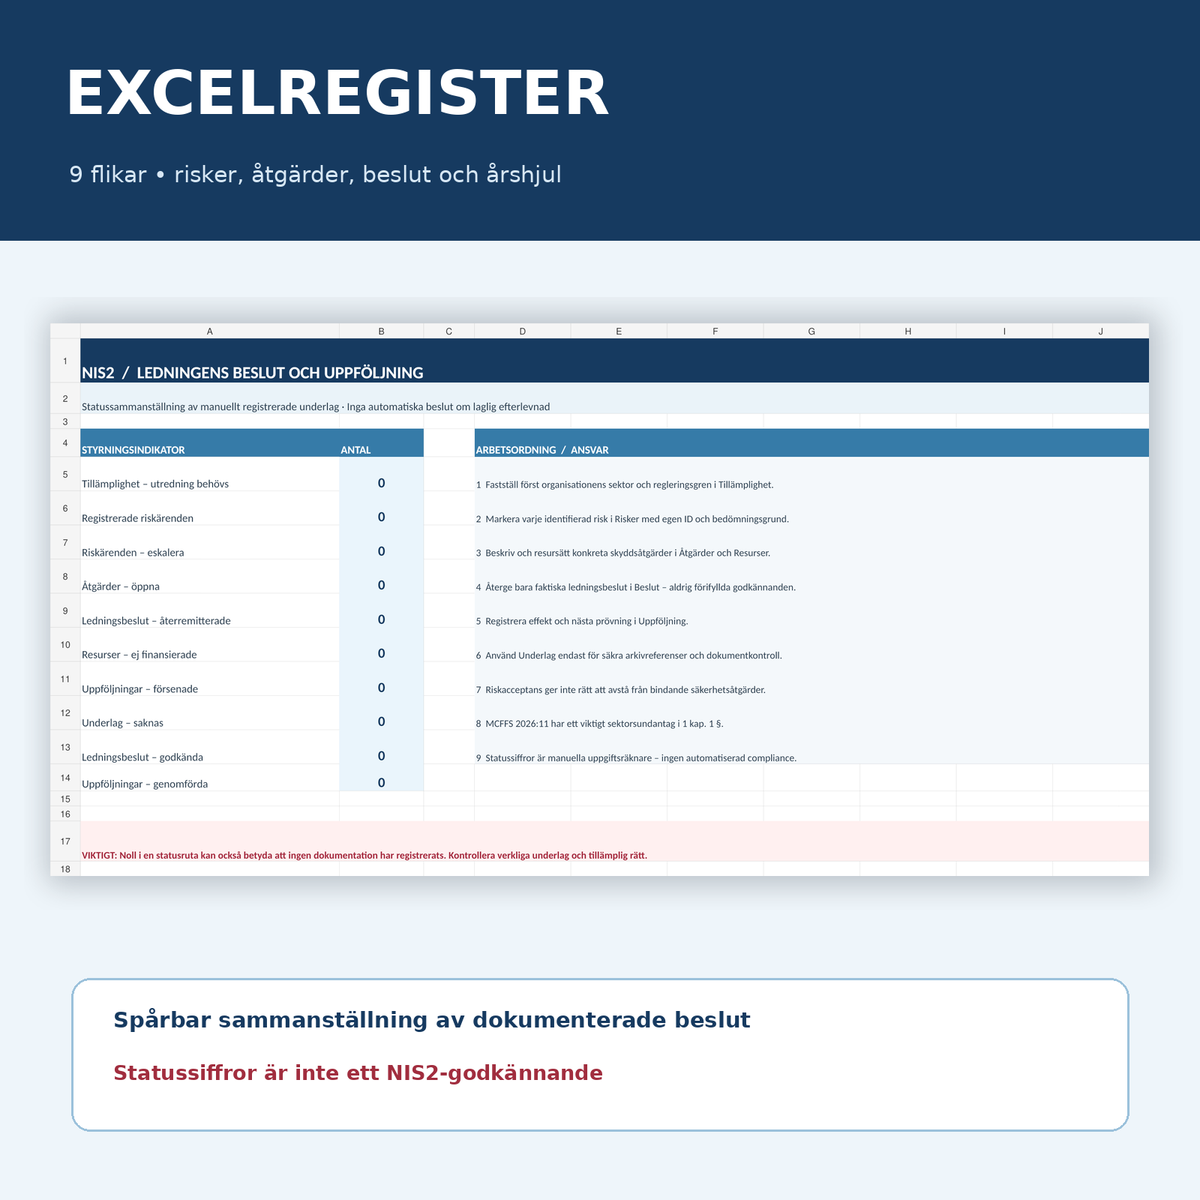
| 08 NIS2 Excel register | Overview and tables for applicability, risks, measures, decisions, resources, follow-up, and basis. | Swedish – editable XLSX |
Excel register with nine tabs
Overview, Applicability, Risks, Measures, Decisions, Resources, Follow-up, Basis, and Read me. The overview uses tested calculations to show manually registered open measures, risk items for escalation, returned management decisions, missing funding, delayed follow-up, and missing basis. Editable status fields have drop-down lists. The customer file is free from synthetic test data.
Important distinction: zero failed items can also mean that nothing has been registered. The formulas do not make a NIS2 assessment and do not allow any automatic approval.
Eight-step workflow
- Check whether the current legal entity is covered by the Cybersecurity Act and identify the sector and applicable regulation.
- Collect current risk analyses, control plans, incident results, and relevant training evidence.
- Prepare a concrete decision memo with identified options and budget.
- Assess which security measures are legally mandatory and which assessments remain.
- Let competent management make the actual decision according to the organization's procedure.
- Register decisions, resources, responsible parties, deviations, and basis with unique IDs.
- Follow implementation and actual effect according to applicable requirements and internal routines.
- Re-evaluate in case of changed risk profile, major incident, supplier shortage, or new regulatory framework.
Current legislation and an important sector difference
The Cybersecurity Act (2025:1506) has applied since January 15, 2026. The Act's Chapter 2, Section 3 applies to appropriate and proportionate technical, operational, and organizational security measures, and Chapter 2, Section 4 to management training. Article 20 of the NIS2 Directive provides the EU law background for management approval and oversight, but the actual Swedish application must be assessed against Swedish law and the relevant sector's regulations.
MCFFS 2026:11 has applied since October 1, 2026. According to Chapter 3, Section 4, when the provision is applicable, management shall approve and oversee the implementation of measures, and be informed as needed, but at least once a year. Chapter 3, Sections 12–13 deal with risk criteria and measure plans, among other things. The provision on management establishing certain risk acceptance criteria in connection with Chapter 3, Section 4 is found among the general advice, which has a different legal status than binding regulations.
Note the sector exemption in MCFFS 2026:11, Chapter 1, Section 1: For operators who exclusively conduct certain listed sector activities, including digital infrastructure, digital providers, and management of ICT services between companies, only the provision on management training in Chapter 2, Section 1 of these regulations applies. Other sector rules and EU implementing acts may still apply. One therefore cannot automatically apply MCFFS Chapter 3, Section 4 to all NIS2 businesses.
The authority's guidance on management's role describes how the competent management body differs between, for example, limited companies, authorities, municipalities, and regions. There is not a single statutory protocol format that fits all business forms. Use the template's minutes as adaptable support and check your own decision rules.
Difference from Mallbutiken's existing NIS2 products
The general NIS2 package provides broad cybersecurity templates. This specialist product is instead about the **board's or management's decision-making and follow-up track**, especially how a measure is actually decided, funded, and re-evaluated. Training and incident packages are separate features that may be needed in parallel.
Frequently asked questions
Does the law require exactly this type of board minutes?
No. What is relevant is that the legally competent management meets the applicable requirements. The template's minutes are a practical way to document a decision and should be adapted to the organization's own formal rules.
Can we approve a risk instead of implementing a mandatory measure?
No. An internal risk acceptance decision is not a waiver from the Cybersecurity Act or other binding requirements. If a mandatory measure is missing, this should be documented as a measure/escalation need.
Does the requirement for management information at least annually apply to all NIS2 companies?
Not as a general statement based on MCFFS 2026:11. Check the regulation's scope, including Chapter 1, Section 1, and other sector-specific rules.
Is this a NIS2 certification?
No. Neither the documents, filled-in minutes, nor Excel calculations constitute certification or evidence of full compliance.
Are the PDF files digitally fillable?
No. The PDF files are searchable and printable references. Fill in the Word/Excel files for digital editing.
Are all five work templates available in English?
No. The five work templates and Excel are in Swedish. An English User Guide explains the workflow and terms in English.
Sources, review level, and version
Official sources: Swedish Parliament, MCF/NCSC – MCFFS 2026:11, MCF/NCSC – management guidance, and the NIS2 Directive.
Product version 1.0 – November 12, 2026. AI-assisted legal source check and file QA performed. No independent external legal review, security audit, authority confirmation, or guarantee of regulatory compliance. The digital customer ZIP should be linked to the download function before any future publication; the link and sales channels are not activated in this draft.