Svenska Dokumentmallar
NIS2 MFA in OT 2026 – vendor access, emergency access and audit logs | Word/PDF/Excel
NIS2 MFA in OT 2026 – vendor access, emergency access and audit logs | Word/PDF/Excel
- File format
- DOCX, PDF, XLSX
- Document language
- Five Swedish work templates + Swedish user guide English User Guide for Swedish templates and Swedish Excel register
- Number of files
- 7
Digital download. No physical product is shipped.
Couldn't load pickup availability
About this template
Do you have system administrators, external service technicians, or emergency accounts that can access the production environment? Sweden's new regulations make it important to be able to show where MFA is required, where it is verified, and what happens when an access path fails the check. This niche Word/PDF/Excel package helps businesses document MFA for IT/OT segments, remote access for suppliers, account lifecycle, secure emergency access, deviations, and re-testing.
Current regulatory framework: The Cybersecurity Act (2025:1506) came into force on January 15, 2026. MCFFS 2026:11 applies from October 1, 2026 and contains specific obligations in Chapter 4, Sections 14–17, with a specific MFA requirement in Section 17. Internal corporate risk acceptance does not replace a binding regulation.
Package contents
01 Scope and MFA requirements – IT, OT, admin, and external network. 02 Privileged accounts and supplier access. 03 Emergency access and controlled backup process. 04 MFA deficiency, remediation, and potential authority exemption question. 05 MFA acceptance test, evidence, and re-testing. 06 Swedish user guide. 07 English User Guide for the Swedish work templates. All seven documents are delivered as editable Word (DOCX) and searchable, printable PDF. 08 Excel register with nine tabs. Total 15 customer files: 7 DOCX + 7 PDF + 1 XLSX.
What the files contain
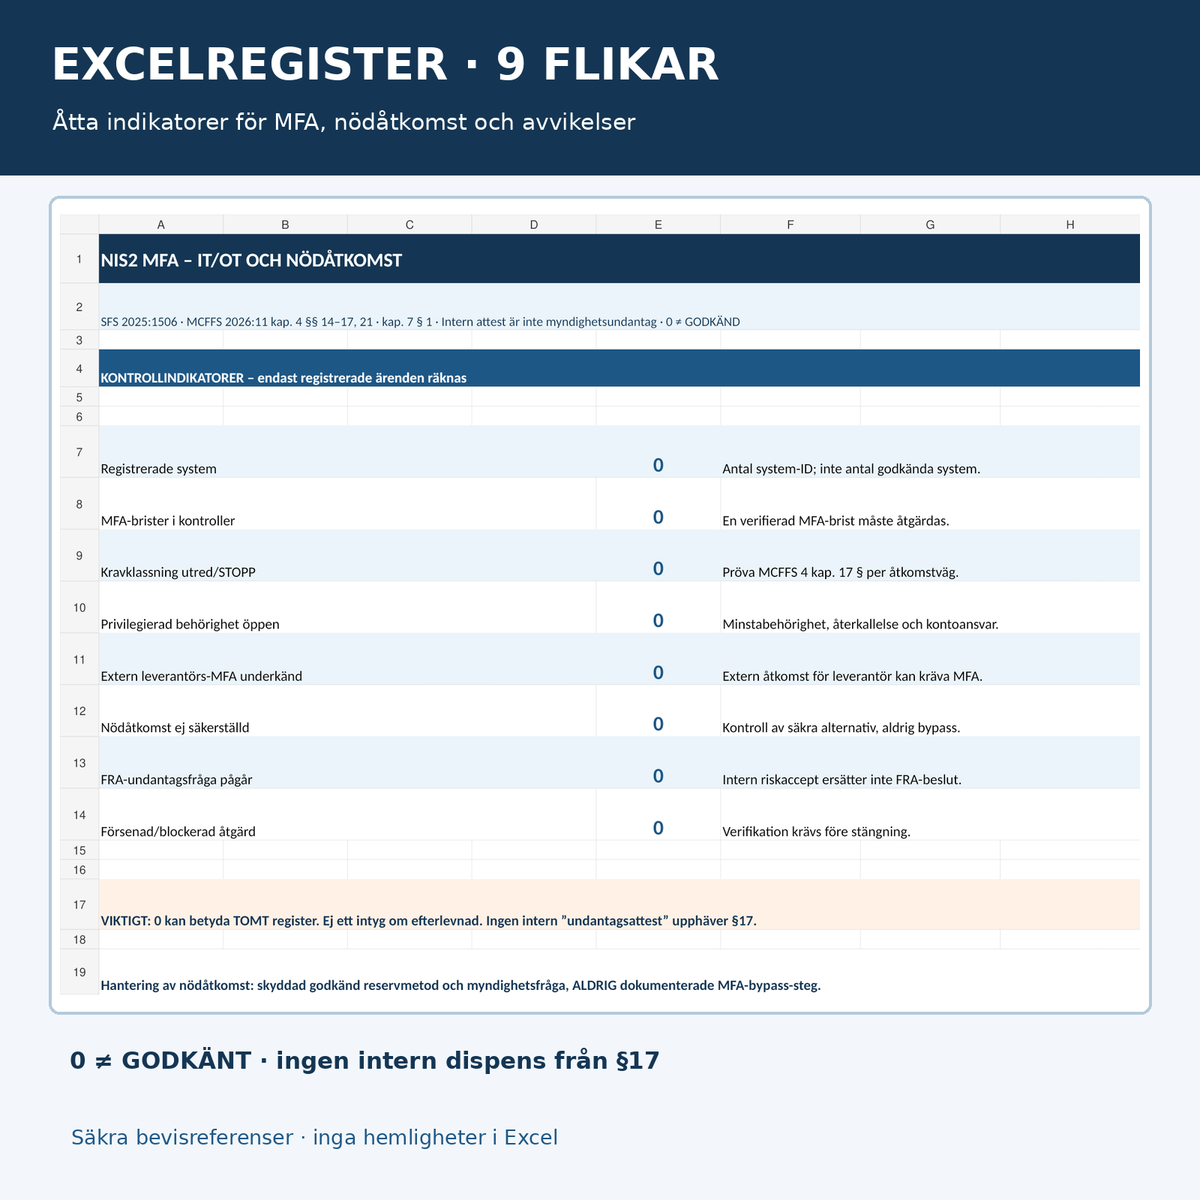
Control matrix for Chapter 4, Section 17 of the regulation, classification of access paths, register of privileged access, supplier permissions and assignment period, MFA configuration evidence, deviations, protected emergency process, verified re-test, audit trail, and remediation owner. Each work template has specific stop signals and a decision/evidence log. Excel contains status selections, eight counters, and a clear distinction between internal remediation and a formal FRA exemption question.
Who needs the document package?
For Swedish operators covered by the Cybersecurity Act and MCFFS 2026:11, especially energy, water, industry, transport, healthcare, digital infrastructure, and other organizations with IT/OT segments. The organization's security officers, system owners, IT/OT administrators, IAM/PAM functions, operations providers, and internal audit can also use the documentation structure. Not all companies are covered by the NIS2 rules; applicability must be assessed first.
Important sector limitation (MCFFS 2026:11, Chapter 1, Section 1): For operators exclusively active in digital infrastructure, digital providers, business-to-business ICT service management, postal and courier services, or space, this particular regulation applies only through Chapter 2, Section 1 on management training. Other obligations may still apply. Assess all actual sector activities before treating this package's MFA controls as a list of binding duties.
File by file – the workflow
| Document | Practical function | Format |
|---|---|---|
| 01 Applicability and MFA requirements | Assess the scope of the law, production environment, IT/OT administration, protected information, and external access. | SV Word + searchable PDF |
| 02 Privileges and suppliers | Basis for restrictive system administration, limited supplier rights, account lifecycle, and evidence ID. | SV Word + PDF |
| 03 Emergency access | Document a pre-verified and controlled backup process without instructions to bypass MFA. | SV Word + PDF |
| 04 Deficiency and exemption question | Record insufficient MFA, remediation, responsible function, and potential separate formal question to FRA. | SV Word + PDF |
| 05 Acceptance and re-test | Plan approved control tests, log trails, and verification without testing in a real OT environment without authorization. | SV Word + PDF |
| 06 Swedish user guide | Step by step, legal sources, and six illustrative control scenarios. | SV Word + PDF |
| 07 English User Guide | English instructions for the five Swedish work templates. The work templates are not translated into English. | EN Word + PDF |
| 08 Excel register | Nine tabs: systems, MFA requirements, privileges, suppliers, emergency access, deviations, actions, overview, and instructions. | SV XLSX |
Excel: nine tabs and eight control indicators
Systems, MFA requirements, Privileges, Suppliers, Emergency access, Deviations, Actions, Overview, and Read me. Formula-based compilation shows, among other things, registered systems, failed MFA checks, open requirement classifications, privilege deficiencies, failed supplier access, insufficient emergency process, ongoing FRA questions, and delayed or blocked actions.
Formulas, status lists, and nine tabs have been verified through synthetic scenario tests. The test tasks have been removed from the customer version. Zero in an empty overview does not mean that the organization complies with the rules.
What does the Swedish regulation require?
The Cybersecurity Act (2025:1506), Chapter 2, Section 3 contains requirements for appropriate and proportionate security measures based on an all-risk assessment, which includes access control and authentication. Read the law at the Swedish Parliament.
MCFFS 2026:11, Chapter 4, Section 17 contains specific MFA requirements for access to IT segments with information that needs enhanced protection, for system administrator access to IT and OT segments in the production environment, and for staff and supplier access to the digital environment via an external network. The need for MFA for other access must also be identified and managed.
Chapter 4, Sections 14–16 cover the lifecycle of identities, blocking of access that has ceased, restrictive administrator rights, and separation between production and test environment credentials. Chapter 4, Sections 20–21 cover security monitoring and logging. Read MCFFS 2026:11 in full.
Important about exemptions: According to Chapter 7, Section 1 of MCFFS 2026:11, the Swedish Defence Radio Establishment (FRA) may, in individual cases and if there are special reasons, grant exemptions from the regulations. This is not the same as an organization itself approving an MFA bypass or replacing a regulation with a signed risk acceptance.
NIS2 Directive Article 21.2 i–j is relevant EU legal background on access control and multi-factor/continuous authentication where appropriate. The Swedish regulations must still be assessed directly. Read Directive (EU) 2022/2555 and NCSC's collection of regulations.
How the package is used
- Assess whether the organization and system are covered by the Cybersecurity Act and any sector-specific regulations.
- Map affected IT/OT segments and identify every access path that must be checked according to Chapter 4, Section 17.
- Review admin and supplier accounts, permission period, identity termination, and follow-up evidence.
- Verify technical MFA in an approved test process and document only secure evidence references.
- Investigate and remediate deficiencies. Conduct a separate legal assessment if a formal authority exemption question arises.
- Document emergency access that meets relevant requirements – without sensitive access credentials in the templates.
- Follow up with re-testing and the eight status indicators in the Excel register.
Frequently Asked Questions
Is MFA always mandatory for administrators in production OT?
MCFFS 2026:11, Chapter 4, Section 17 requires MFA for system administrator access to OT segments in the production environment for operators covered by the regulation. Assess actual applicability and any special authority handling.
Is MFA on the VPN connection enough?
Not necessarily. Both external access and system administrator access are covered by rules that must be assessed based on the respective actual access path.
Can we approve an internal MFA exemption in Excel?
No. An internal risk decision does not override mandatory requirements. Any exemption according to Chapter 7, Section 1 must be handled by FRA under its legal conditions.
Do the files contain passwords, MFA backup codes, or a technical bypass?
No. The template is designed for documenting authorized access and secure evidence references, not for revealing or bypassing protections.
Is this a completed authority application to FRA?
No. Document 04 is an internal remediation and assessment template, not an official application form or authority decision.
Can Excel technically check if MFA works?
No. Excel shows manually registered statuses. The actual technical check must be performed by authorized personnel in an approved environment.
Are the PDF files fillable?
The PDF files are searchable and printable but are not interactive forms. Edit the Word and Excel originals.
Are the templates included in English?
The five work templates and Excel are in Swedish. English User Guide explains how the files are used.
Related document templates
NIS2 Template Package – Cybersecurity Act for broader overall governance. Privilege Audit and Access Review for general access control. NIS2 – Supplier Cyber Certificate for broad supplier follow-up. This product is narrower: binding MFA requirements in IT/OT, actual supplier access, and controlled emergency process.
Version and legal transparency
Version 1.0 · November 12, 2026 · Sweden. AI-assisted source check against SFS 2025:1506, MCFFS 2026:11, EU's NIS2 Directive, and NCSC/FRA authority information. No external legal review, real IT/OT security testing, authority exemptions, IAM audit, or official certification has been performed. The individual organization is responsible for legal and technical application and secure handling of evidence. The product is active in Shopify and a ZIP file is attached in Digital Products. An independent test purchase and customer download have not yet been verified.