Svenska Dokumentmallar
SaaS Agreement Template 2026 – Swedish Law Word/PDF | SLA & GDPR
SaaS Agreement Template 2026 – Swedish Law Word/PDF | SLA & GDPR
- File format
- DOCX, PDF
- Document language
- Swedish
- Number of files
- 1
Digital download. No physical product is shipped.
Couldn't load pickup availability
About this template
SaaS agreement under Swedish law – complete B2B template in Word and PDF
A professional and comprehensive SaaS agreement for Swedish companies selling or buying cloud-based software, subscription services, and other Software as a Service solutions. The template is structured as a complete contractual framework and regulates not only the right to use the software, but also service levels, support, personal data, information security, subcontractors, intellectual property rights, liability, termination, and exit.
You receive both an editable Word file (DOCX) and a ready-to-use PDF version. The document is designed for B2B relationships and can be used by both SaaS providers and corporate clients looking for a structured and clear agreement.
What is included in the package
A SaaS agreement for B2B with a master agreement and six integrated annexes, totaling 15 A4 pages according to the current content overview.
- 1 DOCX: editable Word template.
- 1 PDF: corresponding document for printing and review.
- 1 ZIP: combined download with DOCX and PDF.
- Language: Swedish. Document version: 1.0 (2026).
Digital Products offers the ZIP file and the two documents separately. The six annexes are parts of the contract document, not six extra standalone DOCX files.
What the files contain
The master agreement sets out the parties' rights and obligations. The six annexes are used to specify the service, service levels, personal data processing, security requirements, exit, and price. The Word file allows for entering information, adjusting alternative clauses, and negotiating commercial terms.
Master agreement with 32 contractual areas and six annexes
The SaaS template consists of a master agreement with 32 contractual areas and six practical annexes. In total, the document comprises 15 professionally designed A4 pages with ready-made clauses, alternatives, tables, fill-in fields, and checkpoints.
The master agreement covers, among other things
- parties, background, and definitions,
- order of priority of contract documents,
- scope of service and implementation,
- license and right of use,
- user accounts and authorizations,
- commitments of the provider and the customer,
- availability, maintenance, and SLA,
- support and incident prioritization,
- changes to the SaaS service,
- customer data and data rights,
- GDPR and personal data processing,
- subcontractors and sub-processors,
- third-country transfers,
- information and cybersecurity,
- backup and recovery,
- intellectual property rights and customizations,
- infringement claims,
- confidentiality,
- fees, invoicing, and price adjustments,
- defects, warranty, and remediation,
- limitation of liability and liability caps,
- force majeure,
- contract period and termination,
- suspension of the service,
- exit and data return,
- audit and verification,
- assignment, notices, Swedish law, and dispute resolution.
Annex 1 – Service specification and order form
This defines what the customer is actually purchasing. The annex contains fields for service name, business purpose, included modules and features, number of users, data volume, operating region, implementation, integrations, documentation, and explicit exclusions.
There are also ready-made tables for functional requirements, acceptance criteria, milestones, and technical dependencies. This reduces the risk of disputes regarding what is actually included in the subscription.
Annex 2 – Service Level Agreement (SLA)
A separate SLA is included and can be adapted to the service level of the service. The annex includes, among other things:
- monthly availability targets,
- planned maintenance windows,
- RPO and RTO,
- incident classes P1–P4,
- first response time,
- recovery targets,
- status updates,
- service credits for lack of availability,
- excluded time and emergency security measures.
Annex 3 – Data Processing Agreement (DPA) according to Article 28 GDPR
For many SaaS services, the provider processes personal data on behalf of the customer. In such cases, Article 28 of the GDPR requires a binding agreement between the controller and the processor. Therefore, the template contains a complete DPA annex/data processing agreement.
The annex includes, among other things, the subject matter and duration of the processing, purpose, categories of data subjects, types of personal data, special categories, instructions, confidentiality, technical and organizational security measures, sub-processors, rights of data subjects, personal data breaches, DPIA, third-country transfers, auditing, as well as deletion and return.
Annex 4 – Information and cybersecurity requirements
A practical security annex makes it possible to agree on concrete security requirements instead of a vague formulation about "appropriate security." The checkpoints address, among other things:
- security governance and risk management,
- role-based access and MFA,
- encryption,
- security logging and retention,
- vulnerability and patch management,
- secure development lifecycle,
- backup and recovery,
- incident management,
- BCP and disaster recovery,
- supply chain security,
- personnel security,
- physical security,
- penetration tests,
- ISO 27001, SOC 2, or other agreed verification.
The annex is designed so that additional requirements can be added for customers covered by, for example, the Cybersecurity Act/NIS2. The Swedish Cybersecurity Act (2025:1506), which has been in force since January 15, 2026, includes requirements for supply chain security for businesses covered by the act.
Annex 5 – Exit, data export, and certificate of deletion
The exit issue is often forgotten when a SaaS agreement is signed. This template regulates from the very beginning how the customer will be able to leave the service.
The annex contains fields for export period, export format, metadata, API export, secure transfer, costs, migration support, and deletion. In addition, there is a specific certificate of deletion for production environments, test environments, support copies, and backups.
Annex 6 – Price annex and change log
Ready-made price annex for base fee, users, implementation, premium support, over-usage, consulting time, and exit support. A version and change log makes it easier to document future changes to the agreement.
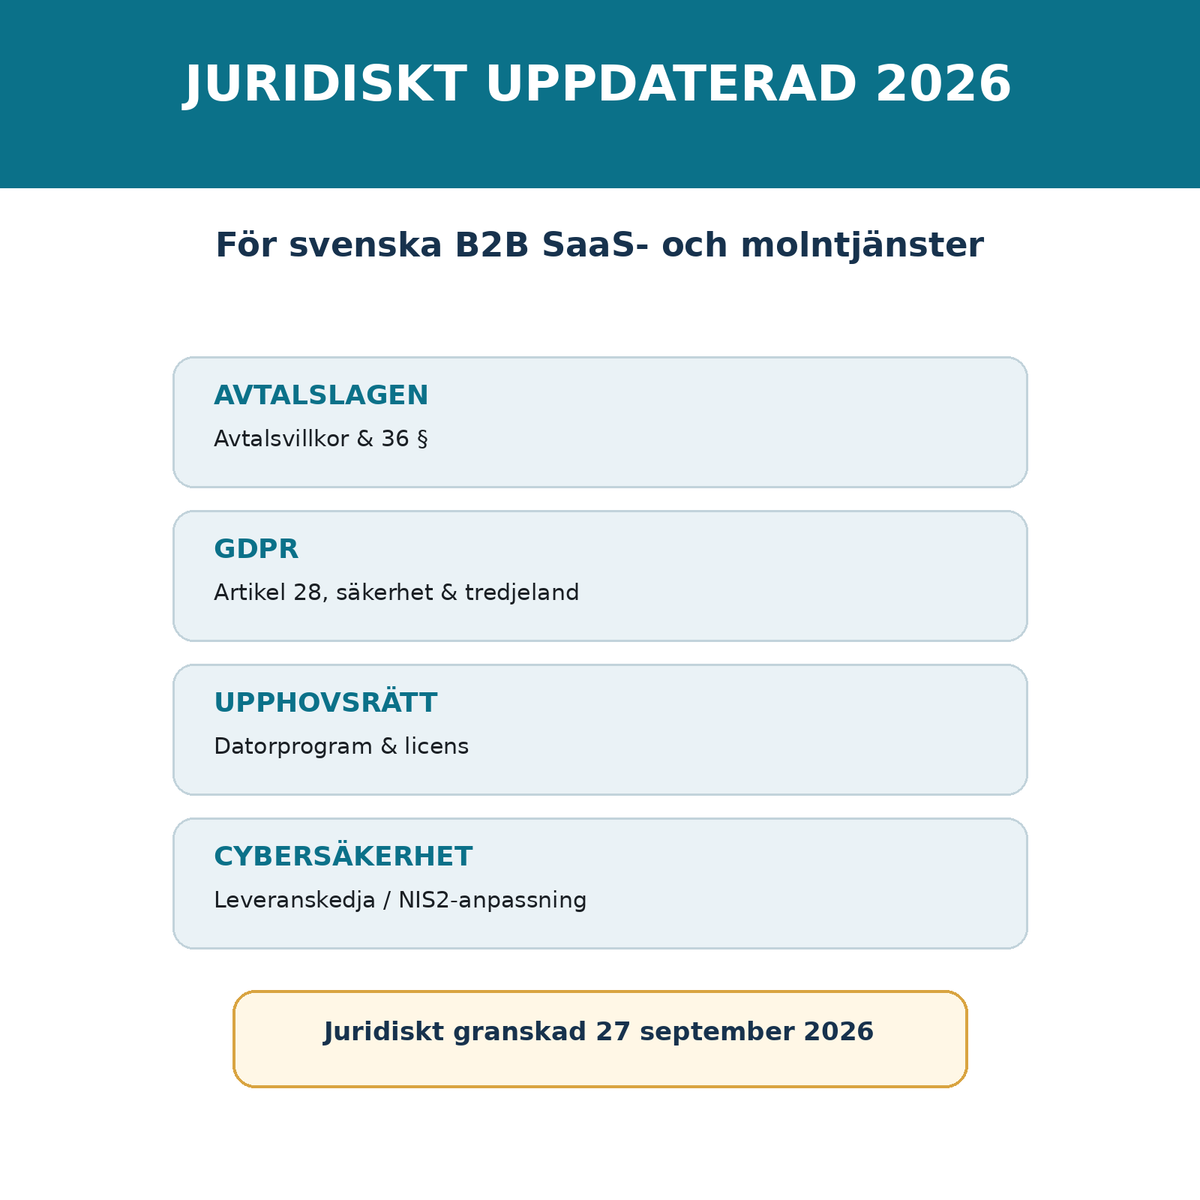
Legally updated for 2026
Version 1.0 has been legally reviewed on September 27, 2026. The template has been designed with consideration for, among other things:
- The Contracts Act (1915:218) – including contract formation and Section 36 regarding unfair contract terms,
- The Copyright Act (1960:729) – including rules concerning computer programs and licensing,
- GDPR (EU) 2016/679 – specifically Article 28 regarding processors, Article 32 regarding security, and rules on third-country transfers,
- Swedish supplementary data protection legislation,
- The Cybersecurity Act (2025:1506) – relevant for agreements with businesses covered by NIS2 rules.
The guidance from the Swedish Authority for Privacy Protection (IMY) on data processing agreements and third-country transfers has also been taken into account.
Liability caps and risk distribution – not an arbitrary default value
The template contains options for liability caps but leaves the actual percentage open for customization. An appropriate liability cap depends on factors such as contract value, data sensitivity, customer operations, cyber risk, insurance coverage, and potential damage. The document therefore reminds the user to specifically assess exceptions for, for example, confidentiality, personal data breaches, intellectual property claims, as well as intent and gross negligence.
Who is the SaaS agreement suitable for?
The template is suitable for, among others:
- SaaS companies and software firms,
- startups and scaleups,
- IT consulting firms that sell their own cloud services,
- companies that buy business systems and web-based services,
- providers of CRM, HR, finance, analysis, and automation systems,
- companies that need a standard agreement for corporate clients or procurement.
Word and PDF
- 15 professionally designed A4 pages
- Editable Word file (DOCX)
- PDF version
- 32 contractual areas
- 6 integrated annexes
- Ready-made tables and fill-in fields
- Alternative clauses where risk distribution needs to be chosen
- Signature section
- Legal checklist before signing
- Sources of law and version information
Important regarding customization
SaaS agreements are heavily influenced by the specific service and the activities of the parties. A simple project platform and a business-critical cloud service for healthcare, finance, or socially critical operations should not have identical contractual terms.
The template must therefore be adapted to actual functionality, information classification, customer data, SLA, subcontractors, operating region, liability, insurance, and any sectoral requirements. It is a professional contractual foundation but does not replace individual legal advice in particularly complex or high-risk business deals.
Digital delivery
After purchase, the customer receives:
- SaaS_agreement_Swedish_law_2026.docx – fully editable Word template
- SaaS_agreement_Swedish_law_2026.pdf – ready-to-use PDF version
The product is delivered digitally. No physical product is shipped.
In-depth: SaaS, SLA, data protection, and security
Before you adapt the agreement, you can use the guide what a SaaS agreement should contain. To select reasonable availability targets, incident classes, and RTO/RPO, there is a special guide on SLA for SaaS services.
For personal data issues, see when a data processing agreement is required and the difference between controller and processor. For security-critical deliveries, the guide NIS2 requirements in supplier agreements provides further support.
Frequently asked questions
Is this just a license agreement?
No. It is a complete SaaS agreement with service specification, SLA, GDPR/DPA, security, exit, and commercial terms.
Is a data processing agreement included?
Yes. Annex 3 is an integrated DPA annex adapted to Article 28 GDPR.
Can the agreement be used by both the provider and the customer?
Yes. The clauses are designed as a balanced B2B basis, and several commercial risk points contain selectable options.
Is the agreement adapted for NIS2?
The agreement includes a security annex and supply chain requirements that can be used as a basis for NIS2-related customer requirements. However, a business covered by the Cybersecurity Act must always adapt the agreement to its own risk analysis and any regulations.
Can I edit everything?
Yes. The Word version is fully editable and contains clear brackets and tables for items that need to be customized.
How are the agreement and annexes distributed between the files?
The master agreement and six annexes are collected in an editable Word file with a corresponding PDF. A ZIP file contains the same two formats. It is therefore not six separate Word annexes.
Is the integrated DPA annex sufficient for every SaaS service?
No. If the provider processes personal data on behalf of the customer, contractual terms, instructions, and security measures must be adapted to the actual processing. Some SaaS relationships may also require a different role assessment according to the GDPR.