Svenska Dokumentmallar
Data Processing Agreement Template Package 2026 – DPA Word/PDF
Data Processing Agreement Template Package 2026 – DPA Word/PDF
- File format
- DOCX, PDF
- Document language
- Swedish
- Number of files
- 5
Digital download. No physical product is shipped.
Couldn't load pickup availability
About this template
Data Processing Agreement 2026 – complete DPA / DPA according to GDPR Article 28
A data processing agreement is required when an external supplier processes personal data on an organization's behalf. This may apply to cloud services, IT operations, web agencies, payroll systems, CRM, customer support, email platforms, analytics tools, and other services where the supplier actually processes personal data under the instructions of the controller.
This template package is designed for Swedish companies and organizations that want to properly document the processor relationship – not just write a short standard agreement. The package's previous table of contents describes five document types in Word and PDF totaling 26 A4 pages. Separate download is verified only for the main agreement and the ZIP archive.
Included in the package
Three verified download items are linked to the product:
- 01_DataProcessingAgreement_DPA_2026.docx – editable main agreement.
- 01_DataProcessingAgreement_DPA_2026.pdf – corresponding PDF.
- DataProcessingAgreement_DPA_TemplatePackage_2026_WORD_PDF.zip – bundled archive.
According to the previous package overview, five document types are included with ten Word/PDF versions totaling 26 pages. The internal file list of the ZIP archive has not been inventoried, which is why these additions cannot be confirmed as separate download files. Swedish, version 1.0.
What the files contain
The main agreement regulates processing instructions, liability, confidentiality, security, sub-processors, incidents, audits, and how personal data should be handled at the end of the agreement. The published package overview also describes separate support for processing instructions, security measures, sub-processor registers, and supplier follow-up; their exact files inside the ZIP need to be verified.
Five document types according to the existing table of contents
- Data Processing Agreement / DPA 2026 – main agreement with 22 clauses and four integrated contract annexes.
- Processor Instruction & Processing Annex – worksheets for role check, processing, data flows, storage, instructions, and communication channels.
- Security Annex / TOM – detailed template for technical and organizational security measures.
- Sub-processor & Third-Country Register – register, TIA screening, change notification, and approval/objection process.
- Supplier Audit, Incident & Deletion – due diligence, incident form, support for data subject requests, deletion certificates, and annual follow-up.
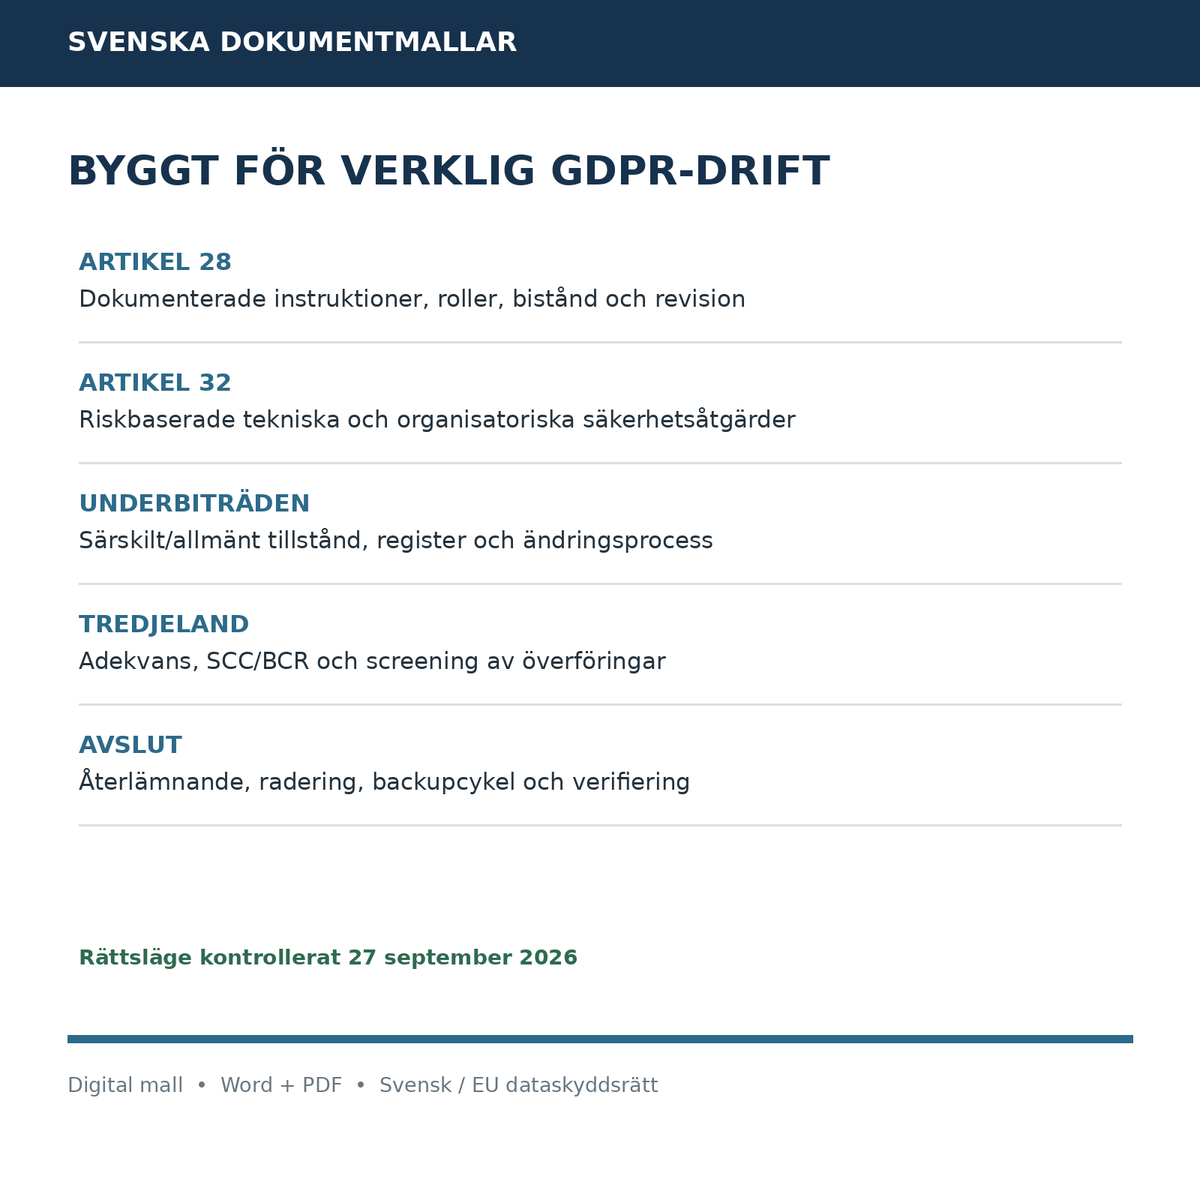
Designed for the minimum requirements of GDPR Article 28
The main agreement regulates the central requirements that must be present in an agreement between a controller and a data processor. This includes, among other things, the subject matter and duration of the processing, the nature and purpose of the processing, categories of data subjects and types of personal data, as well as the rights and obligations of the controller.
The agreement also contains provisions stating that processing may only take place according to documented instructions, confidentiality, appropriate security measures, sub-processors, assistance with data subject rights, support for obligations under GDPR Articles 32–36, deletion or return at the end of the agreement, and the controller's right to information, audits, and inspections.
Documented instructions
A common weakness in general DPA agreements is that the processing is described too vaguely. The package therefore contains a specific processing instruction where the parties can document exactly which service and processing is covered, why the processing takes place, which systems are used, which data subjects are affected, which personal data is processed, and how long the data should be stored.
There is also a separate instruction table where each processing operation can be linked to a system, permitted action, and retention period. This makes it easier to demonstrate what the processor has actually been tasked to do.
Role check – controller or processor?
It is not enough for the parties to call the supplier a data processor. Roles under the GDPR are determined by the actual circumstances. The processing annex therefore contains a practical role check with questions about who determines the purpose, who determines the essential means, and whether the supplier uses data for their own independent purposes.
This helps the buyer detect situations where a supplier may be an independent controller for a certain processing operation or where further regulation needs to be considered.
Sub-processors
The agreement contains two clear options for sub-processors: specific written authorization for each sub-processor or general written authorization with prior information about planned additions and changes.
The separate sub-processor register contains fields for supplier, service, data, data subjects, processing country, and approval. The package also includes a ready-made change notification that the processor can use when a new or changed sub-processor is to be introduced, as well as a structure for the controller's approval or objective data protection objection.
Third-country transfers and SCCs
International cloud services and support chains may result in personal data being transferred or made accessible outside the EU/EEA. The template therefore has a separate third-country register and a practical screening for international transfers.
The register can document recipients, country, role, affected data, transfer mechanism under Chapter V of the GDPR, and any supplementary protection measures. The screening section helps the organization check, among other things, adequacy decisions, SCCs, the right module, supplementary protection, and onward transfers.
Important: this template does not reproduce the European Commission's Standard Contractual Clauses verbatim and is not marketed as an unaltered SCC document. If official SCCs are used for a third-country transfer, the relevant original clauses must be used according to the European Commission's instructions.
Security Annex / TOM
The package's security annex makes it possible to document technical and organizational measures in a concrete way. It covers, among other things, security management, identity and access, MFA, encryption, key management, system and application security, patching, logging, backup, continuity, incident management, personnel, suppliers, physical security, data minimization, and deletion.
Each security requirement can be marked as fulfilled, partially fulfilled, or not fulfilled and supplemented with a description or evidence. There are also fields for certifications, penetration tests, independent audits, open risks, and customer-specific additional requirements.
Personal data breaches
The data processor shall notify the controller without undue delay after becoming aware of a personal data breach. The main agreement therefore contains incident clauses and the possibility of agreeing on a shorter internal target deadline for initial notification.
The operational document contains a specific incident form for time, affected systems, categories of data subjects and personal data, approximate number of records, likely consequences, damage mitigation measures, evidence/logs, and next update.
Data subject rights and assistance
The processor shall, taking into account the nature of the processing, assist the controller in fulfilling obligations towards data subjects. The package therefore contains a specific case template for, for example, access, rectification, erasure, restriction, portability, and objection, with tracking of receipt, forwarding, systems to be searched, and action taken.
Supplier audit before agreement
The controller shall engage processors that can provide sufficient guarantees that appropriate technical and organizational measures are implemented. The package therefore contains a concrete due-diligence checklist for suppliers.
The checklist assesses, among other things, role, security, incident management, sub-processors, third countries, data subject rights, deletion, audit, continuity, and personnel security. The result can be summarized as low, medium, or high risk and documented as approved, conditionally approved, or not approved.
Deletion and return when the agreement terminates
The main agreement and the operational document contain support for the controller's choice between return and deletion. There are special fields for active systems, sub-processors, backup cycles, remaining legal requirements, verification method, and last deletion date.
The separate deletion/return certificate makes it possible to document that the decommissioning has actually been carried out – something that is often missing when a supplier agreement ends.
Audit and inspection
The agreement regulates the processor's obligation to provide information needed to demonstrate compliance and to enable and contribute to audits and inspections. The template allows for practical use of relevant audit reports, certifications, and other verifiable documentation, but without waiving the controller's right under Article 28.
Legal status checked 2026
The legal status has been checked on September 27, 2026. The package has been designed based on the GDPR, specifically Articles 5, 28, 30, 32–36, and 44–49, the Swedish Authority for Privacy Protection's (IMY) current guidance on data processing agreements and the roles of controller/processor, and EDPB Guidelines 07/2020. Consideration has also been given to the European Commission's Implementing Decision (EU) 2021/915 and (EU) 2021/914 where these are relevant.
Word, PDF and ZIP
The main agreement is verified as an editable Word file and corresponding PDF. A ZIP archive contains the package's bundled material, but the archive's internal file list has not been checked during this SEO review.
Digital download without physical delivery.
Guides on GDPR and data processors
First, understand when a data processing agreement is needed and the difference between a controller and a data processor. For international processing, the guide on TIA and SCC for third-country transfers will help.
For procedures during the contract period, read about personal data breaches and notifications as well as retention periods and erasure under the GDPR.
Frequently Asked Questions
Is this the same thing as the European Commission's SCCs for third-country transfers?
No. A DPA according to Article 28 regulates the processor relationship. For certain transfers outside the EU/EEA, a valid transfer mechanism is additionally required, such as relevant official Standard Contractual Clauses.
Must sub-processors be approved?
Yes. According to Article 28 GDPR, specific or general written prior authorization from the controller is required. In the case of general authorization, the processor must inform about planned additions or changes so that objections can be made.
Which individual files can I download?
The main agreement in DOCX and PDF as well as a ZIP archive are verified download objects. The package description specifies additional work documents, but their existence inside the archive has not been checked here.
Important
These are professional legal templates and working documents. The documents must always be adapted to the actual processing, the parties' real roles, information security risks, sub-processors, systems, and any international transfers. In case of complex third-country transfers, sensitive processing, joint controllership, or high risk, individual data protection legal advice should be considered.